
The Cybersecurity Council of the Philippines (CSCP) is giving government agencies, businesses, schools, and local governments a 30-day wake-up call to check their digital defenses, warning that cyberattacks are escalating faster than many organizations can respond.
The urgency is underscored by figures from Viettel Cyber Security, which recorded 16,619 phishing attacks, 255 data breaches, and 21 ransomware attacks in the Philippines during the first half of 2026.
These incidents exposed about 335 million records and compromised more than 19.2 million Filipino account credentials, highlighting how vulnerable personal information and business operations have become.
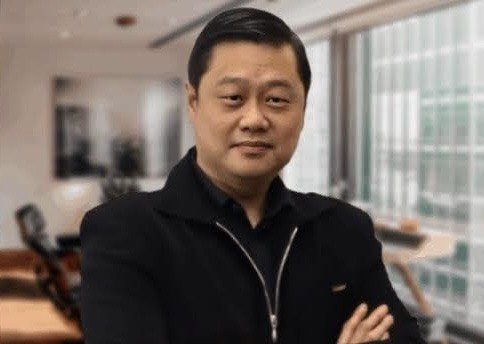
“Hackers do not wait for budgets, for legislation, or for the next board meeting,” said CSCP chairman Donald Patrick Lim, who also heads the Management Association of the Philippines.
Lim urged organizational leaders to stop treating cybersecurity as a technical concern that can be left to IT departments and instead make it an immediate management priority.
The council recommended a series of basic but often neglected safeguards, including installing security updates, enabling multifactor authentication, removing inactive user accounts, and checking whether offline backups can actually be restored.
Organizations should also conduct phishing simulations, restrict suppliers’ access to internal systems, and rehearse incident response plans. To thwart impersonation scams, any changes to payment instructions or fund transfers should be verified through a previously established telephone number.
Beyond immediate fixes, CSCP wants boards, executives, and agency heads to take direct responsibility for cyber risks, appoint security officers, and allocate dedicated budgets.
It is also pushing for cybersecurity education beginning in basic education, faster incident reporting, and stronger threat intelligence sharing across industries, alongside renewed calls for a national cybersecurity law covering critical infrastructure.
The council plans to release a free cybersecurity checklist, organize training for employees and educators, and convene a public-private threat-sharing forum.
The underlying message is that cybersecurity cannot be postponed until the next budget cycle. In a world where one careless click can compromise millions of records, 30 days may already be generous.